
Business Email Compromise: The Invoice Scam Targeting SMEs
Business Email Compromise: The Invoice Scam Targeting SMEs A supplier sends an email advising that its banking details have changed. The address appears correct, the invoice looks familiar and the message refers to a genuine project. The accounts department processes the payment. Days later, the real supplier asks why the account remains unpaid. This is […]
 Tash Bhairo11 September 20263 min read
Business Email Compromise: The Invoice Scam Targeting SMEs
A supplier sends an email advising that its banking details have changed. The address appears correct, the invoice looks familiar and the message refers to a genuine project.
The accounts department processes the payment. Days later, the real supplier asks why the account remains unpaid.
This is business email compromise, commonly abbreviated to BEC. It is one of the most financially damaging forms of cybercrime because it exploits trusted relationships and normal business processes rather than relying only on malicious attachments.
How the scam works
Criminals may use several methods.
They can register a domain that closely resembles the supplier’s real address. They may compromise the supplier’s mailbox and send messages from the genuine account. In other cases, they access the customer’s email and monitor correspondence until the correct moment to insert fraudulent payment instructions.
Because the criminals have observed real conversations, they may know:
- The supplier’s name
- Which employee handles payments
- The expected invoice amount
- The project being discussed
- When payment is due
- The wording normally used in emails
The message can therefore look completely legitimate.
Why antivirus may not stop it
A BEC message may contain no virus, malicious attachment or obvious phishing link. It may simply provide different banking details on a modified invoice.
Traditional antivirus has little to detect. The most effective control is a combination of account security and a strong payment-verification process.
Warning signs to watch for
Treat these situations with caution:
- New banking details
- An unexpected request for urgent payment
- Pressure to keep the transaction confidential
- A subtle change in the sender’s domain
- A reply-to address that differs from the sender
- An invoice that looks slightly different
- A request to bypass normal approval
- Unusual timing or writing style
- Claims that the supplier’s phone is unavailable
A correct-looking email address is not absolute proof. A genuine mailbox may be compromised.
Verify through an independent channel
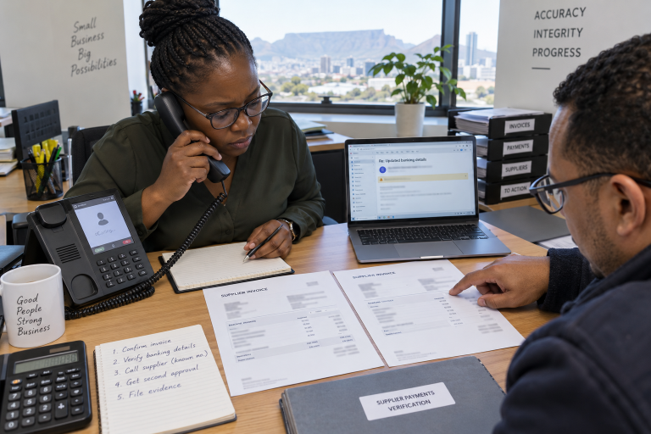
Every bank-detail change should be verified using contact information already held by the business.
Do not phone the number included on the new invoice or in the suspicious email. Retrieve the supplier’s established number from your accounting records, original agreement or trusted website.
The person verifying the change should record:
- Who was contacted
- Which trusted number was used
- Who confirmed the details
- The date and time
- Whether a second person approved the payment
The same procedure should apply to executives and long-standing suppliers. Familiarity is exactly what the criminal is exploiting.
Secure the email environment
Businesses should also:
- Enable multifactor authentication
- Protect administrator accounts
- Review suspicious mailbox rules
- Remove access belonging to former employees
- Configure domain-authentication protections
- Monitor unusual logins
- Train finance staff using realistic examples
- Use dual approval for significant payments
If fraud is discovered, immediately contact the bank, IT provider and appropriate authorities. Speed may affect whether funds can be traced or frozen.
RandTech IT helps South African SMEs secure Microsoft 365, investigate suspicious mailbox activity and implement practical anti-phishing controls.
A professional-looking invoice is not proof of authenticity. When banking details change, pause the payment and verify the request independently. A two-minute phone call can prevent a loss that takes months—or longer—to resolve.
Tash Bhairo
Tash Bhairo leads Randtech IT with nearly two decades of hands-on experience in business support, infrastructure, cloud systems and software development.
Related Insights
How Social Engineering Turns a Trusted Identity Into Payment Fraud
The most dangerous part of an online scam is often not the technology. It is the relationship the…
Cloud Services Still Need a Business Continuity Plan
The debate concerns national infrastructure and development policy, but it also highlights a simpler lesson for small businesses:…
Windows 11 Bluetooth Problems: Fix the Cause Before Replacing Hardware
A wireless headset that stutters, a mouse that disconnects or a laptop that shows the wrong Bluetooth status…