Tag: business email compromise

  • Business Email Compromise: The Invoice Scam Targeting SMEs

    Business Email Compromise: The Invoice Scam Targeting SMEs

    Business Email Compromise: The Invoice Scam Targeting SMEs

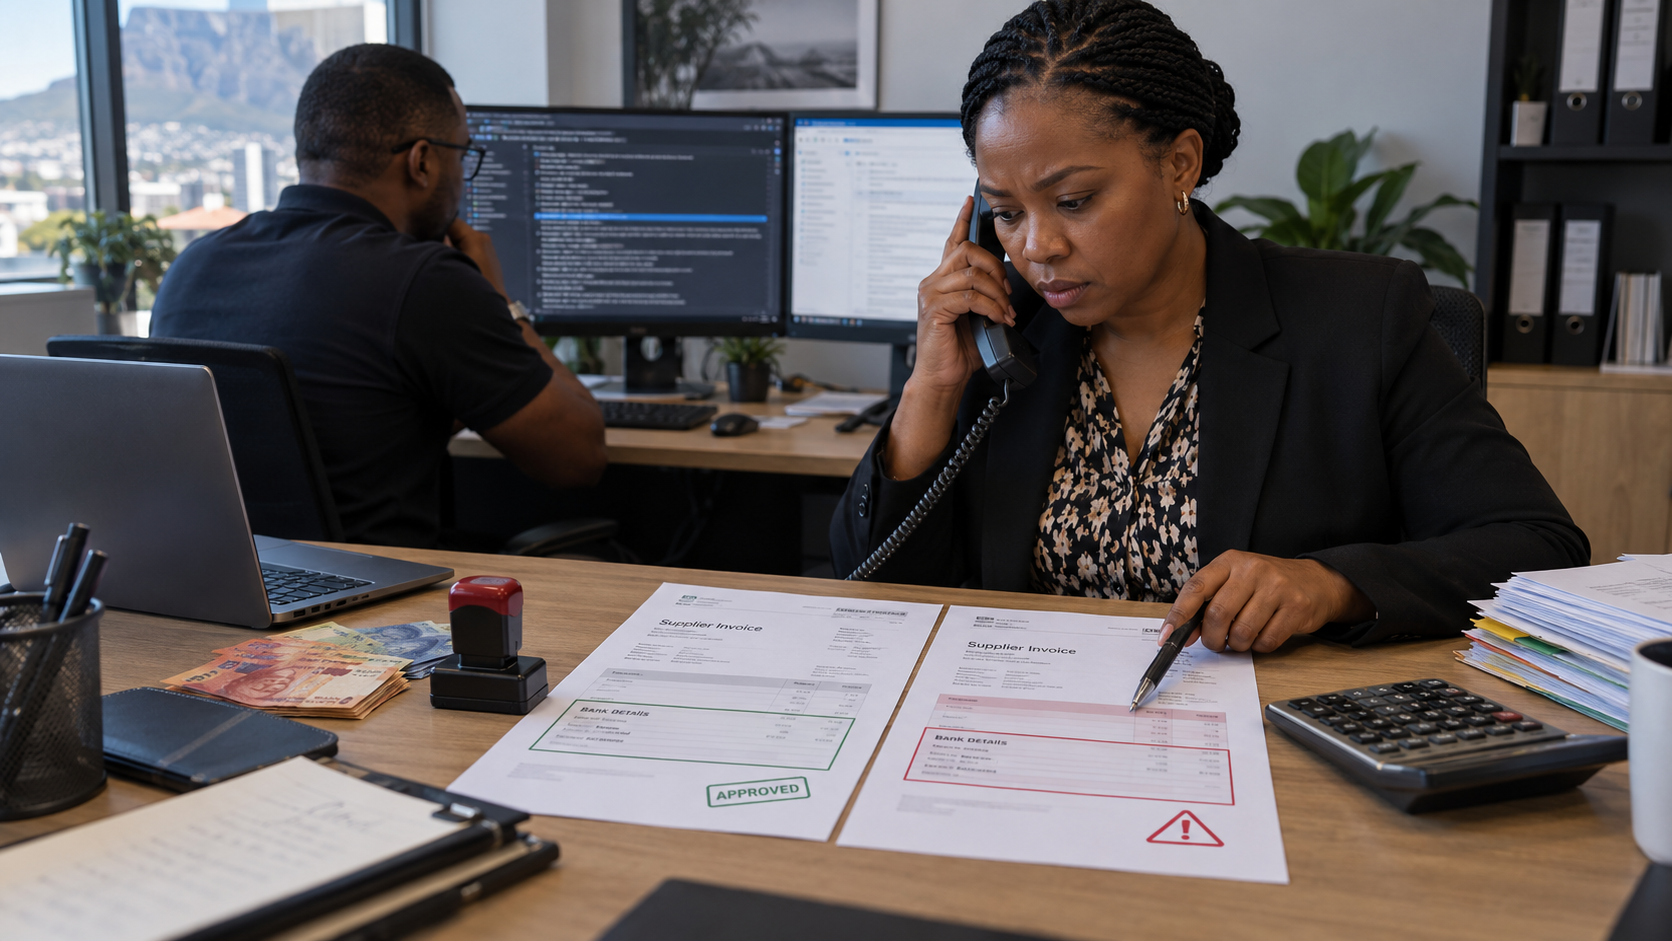
    A supplier sends an email advising that its banking details have changed. The address appears correct, the invoice looks familiar and the message refers to a genuine project.

    The accounts department processes the payment. Days later, the real supplier asks why the account remains unpaid.

    This is business email compromise, commonly abbreviated to BEC. It is one of the most financially damaging forms of cybercrime because it exploits trusted relationships and normal business processes rather than relying only on malicious attachments.

    How the scam works

    Criminals may use several methods.

    They can register a domain that closely resembles the supplier’s real address. They may compromise the supplier’s mailbox and send messages from the genuine account. In other cases, they access the customer’s email and monitor correspondence until the correct moment to insert fraudulent payment instructions.

    Because the criminals have observed real conversations, they may know:

    • The supplier’s name
    • Which employee handles payments
    • The expected invoice amount
    • The project being discussed
    • When payment is due
    • The wording normally used in emails

    The message can therefore look completely legitimate.

    Why antivirus may not stop it

    A BEC message may contain no virus, malicious attachment or obvious phishing link. It may simply provide different banking details on a modified invoice.

    Traditional antivirus has little to detect. The most effective control is a combination of account security and a strong payment-verification process.

    Warning signs to watch for

    Treat these situations with caution:

    • New banking details
    • An unexpected request for urgent payment
    • Pressure to keep the transaction confidential
    • A subtle change in the sender’s domain
    • A reply-to address that differs from the sender
    • An invoice that looks slightly different
    • A request to bypass normal approval
    • Unusual timing or writing style
    • Claims that the supplier’s phone is unavailable

    A correct-looking email address is not absolute proof. A genuine mailbox may be compromised.

    Verify through an independent channel

    Every bank-detail change should be verified using contact information already held by the business.

    Do not phone the number included on the new invoice or in the suspicious email. Retrieve the supplier’s established number from your accounting records, original agreement or trusted website.

    The person verifying the change should record:

    • Who was contacted
    • Which trusted number was used
    • Who confirmed the details
    • The date and time
    • Whether a second person approved the payment

    The same procedure should apply to executives and long-standing suppliers. Familiarity is exactly what the criminal is exploiting.

    Secure the email environment

    Businesses should also:

    • Enable multifactor authentication
    • Protect administrator accounts
    • Review suspicious mailbox rules
    • Remove access belonging to former employees
    • Configure domain-authentication protections
    • Monitor unusual logins
    • Train finance staff using realistic examples
    • Use dual approval for significant payments

    If fraud is discovered, immediately contact the bank, IT provider and appropriate authorities. Speed may affect whether funds can be traced or frozen.

    RandTech IT helps South African SMEs secure Microsoft 365, investigate suspicious mailbox activity and implement practical anti-phishing controls.

    A professional-looking invoice is not proof of authenticity. When banking details change, pause the payment and verify the request independently. A two-minute phone call can prevent a loss that takes months—or longer—to resolve.
    Reference: INTERPOL guidance on business email compromise

  • How to Recognise AI-Generated Phishing Emails in 2026

    How to Recognise AI-Generated Phishing Emails in 2026

    How to Recognise AI-Generated Phishing Emails in 2026

    “Look for bad spelling” is no longer enough to protect a business from phishing.

    Generative AI can produce professional emails with correct grammar, convincing formatting and a tone that sounds like a supplier, manager or colleague. Criminals can combine AI with information from websites, LinkedIn profiles, data breaches and previous email compromises to create highly believable messages.

    INTERPOL’s 2026 African Cyberthreat Assessment says artificial intelligence is enabling cybercrime across Africa to become faster, more scalable and increasingly sophisticated.

    Employees therefore need to judge an email by its request and context—not simply by how well it is written.

    AI makes personalisation easier

    A criminal can quickly gather names, job titles, suppliers and current projects from public sources. AI can then turn that information into a message aimed at one specific employee.

    For example, an accounts user may receive a message appearing to come from a known supplier, explaining that its banking details have changed. A manager may receive a realistic Microsoft 365 login alert. An employee may hear a voice note that resembles an executive asking for an urgent payment.

    The individual details may be accurate even when the request is fraudulent.

    Warning signs still exist

    AI-generated phishing may be polished, but criminals still need the recipient to perform an action. Focus on that action.

    Be suspicious when a message requests:

    • An urgent or confidential payment
    • A change to supplier banking details
    • Login through an unexpected link
    • An MFA code or approval
    • Confidential customer or employee information
    • Installation of remote-access software
    • Purchase of vouchers or gift cards
    • Bypassing the normal approval process
    • Opening an unexpected shared document

    Urgency, secrecy and unusual procedure are stronger indicators than spelling mistakes.

    Check the sender carefully

    A displayed name can be copied easily. Examine the full email address and domain.

    Criminals may use a lookalike domain containing an extra letter, substituted character or different ending. An email may also come from a legitimate account that has been compromised, so a correct address is not absolute proof.

    Do not use the phone number or contact details included in the suspicious message to verify it. Use a number already held in your records or speak to the person directly.

    Treat login links with caution

    Fake Microsoft 365 pages can closely resemble the real sign-in screen. Some attacks also relay authentication in real time or attempt to trick users into approving an MFA request.

    Instead of clicking an unexpected email link, open the service through a saved bookmark or enter the known address manually. Never provide an MFA code to another person or approve a login you did not initiate.

    If a user enters credentials into a suspicious page, report it immediately. Quick action may allow administrators to reset the password, revoke active sessions and investigate before the account is used against customers or colleagues.

    Introduce a second-channel verification rule

    Every business should have a rule for high-risk requests:

    Changes to banking details, unusual payments and requests for confidential records must be confirmed through a second trusted channel.

    A phone call to a known number may feel inconvenient, but it can prevent a major loss. The verification process should apply regardless of whether the email appears to come from the CEO or a long-standing supplier.

    Technology and training must work together

    Email filtering, endpoint security and MFA remain important. However, no filter can guarantee that every well-crafted message will be blocked.

    RandTech IT helps South African businesses strengthen Microsoft 365 security, review suspicious email activity and train employees using realistic examples.

    The new rule is simple: do not trust an email because it looks professional. Verify the identity, request and procedure before money, passwords or sensitive information leave the business.

    Source: INTERPOL’s 2026 African Cyberthreat Assessment