Category: Microsoft 365

  • Cloud Services Still Need a Business Continuity Plan

    Cloud Services Still Need a Business Continuity Plan

    The debate concerns national infrastructure and development policy, but it also highlights a simpler lesson for small businesses: “it is in the cloud” does not mean every dependency has disappeared.

    The Associated Press reported on 5 September that South Africa hosts a substantial portion of Africa’s data-centre capacity and that campaigners are challenging further hyperscale expansion. Reuters had previously reported approval and objections around proposed Equinix facilities in Cape Town on 28 July 2026.

    For an SME in Johannesburg, the immediate risk is usually not the hyperscale facility. It is the fibre line, router, office power, DNS, user account or laptop between the employee and the service.

    Map the full chain

    Ask what is required for staff to open email, process an order or help a customer.

    The chain may include:

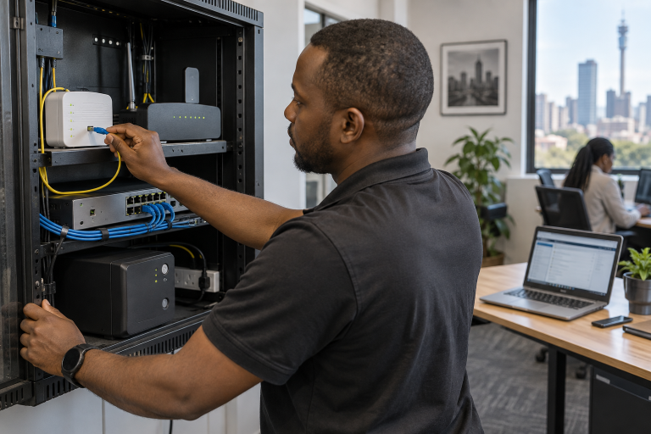
    • Electricity to the office and network cabinet
    • Fibre or fixed-wireless connectivity
    • Router, firewall, switches and Wi-Fi access points
    • Microsoft 365 or another cloud provider
    • Multifactor authentication on an employee’s phone
    • A working, updated laptop
    • Access to files and passwords

    A highly resilient cloud platform cannot compensate for a router that switches off two minutes into an outage.

    Add connectivity failover carefully

    An LTE or 5G connection can keep essential users online when fibre fails, but only if it is configured and tested in advance. Confirm signal quality, data limits, network coverage and whether the router changes connections automatically.

    Failover should prioritise essential services. A software update or cloud backup can consume mobile data while accounts staff are trying to process payments. Appropriate firewall and traffic rules can preserve the link for email, voice and critical applications.

    Size backup power for the network

    Keeping laptops charged does not help when the fibre terminal, router and switch have no power. Identify every network component that must remain on, measure its load and set a realistic runtime objective.

    A UPS battery also degrades. Test it under load and replace it based on condition, not merely age or a green indicator light.

    Prepare a degraded way of working

    Business continuity is not always full restoration. It may mean allowing a smaller group to continue essential work while the main connection is repaired.

    Document who needs priority access, which phone hotspot may be used, how incoming calls are handled, and which files can be securely available offline. Avoid copying uncontrolled customer data onto personal devices as an emergency shortcut.

    Test the plan

    Disconnect the primary internet connection during a controlled window and observe what happens. Can users still authenticate? Does Teams calling work? Can the business reach cloud accounting and retrieve key documents? Record the gaps and repeat the test after remediation.

    RandTech IT helps Johannesburg businesses design and test internet failover, office-network UPS protection and Microsoft 365 continuity. The cloud removes many local server risks, but resilience still depends on the last kilometre—and on a plan that has been proved before the outage.

  • New Outlook vs Classic Outlook: Which Is Better for Business?

    New Outlook vs Classic Outlook: Which Is Better for Business?

    New Outlook vs Classic Outlook: Which Is Better for Business?

    Microsoft is progressively moving Windows users towards New Outlook, but that does not mean every business should switch every employee immediately.

    New Outlook offers a modern interface and a more consistent experience across Outlook on the web and Windows. Classic Outlook remains the established desktop application used by organisations with complex mailbox configurations, legacy add-ins and specialised workflows.

    Microsoft says existing Classic Outlook installations will remain supported until at least 2029. Businesses therefore have time to evaluate the change instead of treating every upgrade prompt as an emergency.

    What New Outlook does well

    New Outlook provides a cleaner interface and receives many of Microsoft’s newest cloud-connected features. Users familiar with Outlook on the web may find the layout easier to understand.

    Potential benefits include:

    • A consistent experience between the browser and Windows application
    • Simplified account and settings management
    • Modern search and calendar features
    • Easier integration with Microsoft’s online services
    • Reduced dependence on some traditional local Outlook components
    • Ongoing feature development from Microsoft

    For users who mainly send email, manage a calendar and work with one or two straightforward mailboxes, New Outlook may be entirely suitable.

    Why some businesses still need Classic Outlook

    Classic Outlook has existed for decades and supports a wide range of mature business workflows.

    A business may need to remain on Classic Outlook where users rely on:

    • Legacy COM add-ins
    • Specialist accounting or document-management integrations
    • Complex shared-mailbox workflows
    • PST files and established archive processes
    • Advanced offline access
    • Custom forms, macros or automation
    • Features that are not yet equivalent in New Outlook

    Compatibility continues to improve, but an apparently small missing feature can have a large operational effect if it sits inside a daily process.

    Shared mailboxes need careful testing

    Many South African SMEs use shared mailboxes for accounts, claims, sales, support or general enquiries.

    Before migration, test how users open the mailbox, send from its address, search older messages, use categories and manage signatures or delegated calendars. Do not assume that a workflow behaves identically merely because the mailbox appears in both applications.

    Businesses with several large shared mailboxes should also review permissions and caching. In Classic Outlook, automatically caching multiple shared mailboxes can produce very large OST files, consume disk space and cause confusing “mailbox full” or synchronisation symptoms even when the server mailbox is not full.

    Can users switch between them?

    In many current installations, users can try New Outlook and return to Classic Outlook. Microsoft’s rollout phases and available controls depend on the Microsoft 365 licence and update channel.

    IT administrators should manage the transition centrally where possible. Allowing each user to switch independently can create inconsistent interfaces, duplicated support work and uncertainty about which features should be available.

    Test before standardising

    A sensible migration process should:

    1. Document important Outlook workflows and add-ins
    2. Select a small pilot group
    3. Test shared mailboxes, printing, search and offline access
    4. Confirm line-of-business integrations
    5. Train users on changed layouts
    6. Keep a controlled fallback path
    7. Expand deployment only after the pilot succeeds

    The best Outlook version is the one that supports the user’s real work reliably.

    RandTech IT helps businesses troubleshoot Outlook, optimise shared-mailbox configurations and plan controlled New Outlook deployments.

    If your staff are receiving prompts to change Outlook, do not click through blindly or block the change forever. Test the new application against your business processes, identify genuine compatibility gaps and move when the organisation is ready.

    Source: Microsoft’s New Outlook adoption guidance

  • Why Your Business Still Needs Microsoft 365 Backup

    Why Your Business Still Needs Microsoft 365 Backup

    Why Your Business Still Needs Microsoft 365 Backup

    Microsoft 365 stores business email, documents, Teams information and SharePoint data in highly resilient cloud infrastructure. That often creates the impression that everything in Microsoft 365 is automatically backed up forever.

    It is not quite that simple.

    Microsoft protects the availability and operation of its cloud platform, while your business remains responsible for how its users, administrators and connected applications handle company information. Deleted data may be recoverable for a limited period, but Microsoft 365 retention features should not automatically be treated as a complete independent backup system.

    Cloud storage and backup are different

    OneDrive synchronises files between a user’s computer and the cloud. SharePoint gives teams a central place to store and collaborate on documents. Exchange Online keeps business email accessible across devices.

    These services are built for productivity and availability. Backup has a different purpose: maintaining a separate recoverable copy of data in case the live information becomes unavailable, corrupted or deliberately removed.

    If a user deletes a synchronised folder, the deletion may be reflected across the environment. If an attacker compromises an administrator account, they may attempt to delete data or weaken retention settings. Malware can also encrypt files before the damaged versions synchronise to OneDrive or SharePoint.

    Microsoft 365 includes recycle bins, version history and retention capabilities, but each feature has rules, limits and configuration requirements.

    Common ways businesses lose Microsoft 365 data

    Data loss is not always caused by Microsoft suffering a major outage. More common causes include:

    • A staff member accidentally deleting a mailbox or folder
    • An employee leaving before important information is transferred
    • A compromised account deleting or manipulating data
    • Incorrect SharePoint permissions exposing files
    • Malware encrypting synchronised documents
    • An administrator changing a retention policy
    • A third-party application corrupting or deleting information
    • The business discovering a loss after the recovery window has passed

    A backup becomes particularly valuable when nobody notices the problem immediately.

    What should be protected?

    A Microsoft 365 backup strategy should account for the services the business actually uses. This may include:

    • Exchange Online mailboxes
    • Shared mailboxes
    • OneDrive accounts
    • SharePoint sites and document libraries
    • Teams files and associated SharePoint data
    • Contacts and calendars

    The system should also make it possible to restore individual items. Recovering one deleted email or folder should not require rebuilding an entire environment.

    Retention and backup solve different problems

    Retention policies are important for governance, compliance and controlling how long information is kept. They can help prevent permanent deletion during a defined retention period.

    Independent backup provides another recovery layer. It can preserve separate copies, offer longer recovery histories and reduce dependence on the state of the live Microsoft 365 tenant.

    Many businesses benefit from using both. Retention helps govern information inside Microsoft 365, while backup provides an additional route to recovery.

    A backup must be tested

    A dashboard showing successful backup jobs is reassuring, but it does not prove that the correct data can be restored quickly.

    Businesses should periodically test:

    • Restoring an individual email
    • Recovering a OneDrive folder
    • Restoring a SharePoint document and its previous version
    • Recovering data belonging to a former employee
    • Confirming who is authorised to initiate a restore
    • Measuring how long recovery takes

    These tests turn backup from a subscription into an operational recovery capability.

    RandTech IT helps South African businesses assess Microsoft 365 retention, implement independent cloud backup and test the recovery of Exchange, OneDrive and SharePoint information.

    Your data may be in Microsoft’s cloud, but it is still your business’s responsibility. A properly configured and tested backup ensures that one mistake, compromised account or late discovery does not become permanent data loss.

    Source: Microsoft 365 Backup documentation

  • Windows 10 and Microsoft 365 Deadlines: What Businesses Must Know

    Windows 10 and Microsoft 365 Deadlines: What Businesses Must Know

    Windows 10 and Microsoft 365 Deadlines: What Businesses Must Know

    Windows 10 reached the end of its standard support lifecycle on 14 October 2025, but many South African businesses still use it every day.

    A Windows 10 computer does not suddenly stop working after support ends. That is precisely why the risk can be easy to ignore. The machine may continue opening email, browsing the internet and running business software while gradually falling behind current security and compatibility requirements.

    Businesses now need to distinguish between three separate issues: Windows security support, Extended Security Updates and Microsoft 365 application support.

    What happened to normal Windows 10 support?

    Microsoft no longer provides ordinary free security updates, feature improvements or technical support for standard Windows 10 installations.

    Eligible devices can receive Extended Security Updates, commonly called ESU, for a limited period. ESU can be useful when a business needs additional time to replace specialist hardware or test important software.

    It should be treated as a transition measure—not as a permanent strategy for keeping ageing computers indefinitely.

    Microsoft 365 has a different timetable

    Microsoft has continued providing security updates for Microsoft 365 Apps running on Windows 10 for a transitional period.

    According to Microsoft’s current lifecycle guidance, Version 2608 is the final Microsoft 365 Apps feature version for Windows 10. Devices remaining on that operating system can continue receiving security updates for that version until 10 October 2028.

    This does not restore full Windows 10 support. It means the Office applications have their own temporary security-update arrangement while the underlying operating system remains outside normal support unless separately covered by ESU.

    Businesses should therefore avoid interpreting “Office still receives updates” as “the computer is fully supported.”

    Should you upgrade or replace the computer?

    Not every Windows 10 PC needs to be discarded.

    A device may support Windows 11 after firmware settings, TPM or Secure Boot configuration has been corrected. In other cases, the processor or security hardware may not meet Microsoft’s requirements.

    A proper assessment should check:

    • Processor and Windows 11 compatibility
    • TPM version and status
    • Secure Boot capability
    • Available RAM and storage
    • SSD health
    • BIOS or firmware updates
    • BitLocker recovery-key availability
    • Application and printer compatibility
    • Age and physical condition of the device

    A technically compatible PC may still be a poor upgrade candidate if its storage is failing, battery is unusable or performance no longer meets the user’s needs. Conversely, a good-quality business laptop with adequate hardware may need only configuration, an SSD or additional memory.

    Avoid unsupported upgrade shortcuts

    Various online methods can install Windows 11 on unsupported computers. They may work, but a business should understand the consequences before relying on them.

    Unsupported installations can introduce uncertainty around future updates, drivers and vendor support. That may be acceptable for a non-critical personal device, but it is a questionable foundation for payroll, accounting, customer service or regulated information.

    Build a controlled replacement plan

    Businesses should inventory their computers and classify them into four groups:

    1. Ready for a normal Windows 11 upgrade
    2. Upgradeable after configuration or hardware improvements
    3. Temporarily retained with ESU
    4. Due for replacement

    This prevents emergency purchasing and allows replacements to be budgeted by business priority.

    RandTech IT provides Windows compatibility assessments, upgrades, data migration and replacement-device planning for South African SMEs. If your business still has Windows 10 computers, now is the time to establish which machines can be upgraded safely and which have reached the end of their practical life.

    Sources: Microsoft’s Windows 10 lifecycle page and Microsoft 365 Apps support guidance

  • Microsoft 365 migration checklist for South African SMBs

    Microsoft 365 migration checklist for South African SMBs

    Introduction

    Moving to Microsoft 365 is a strategic step for South African small and medium-sized businesses (SMBs). It delivers familiar productivity tools, cloud email, and collaboration platforms that can improve efficiency and support remote work. But migrations that lack planning can cause downtime, security gaps, and frustrated staff. This Microsoft 365 migration checklist gives practical, step-by-step guidance tailored to SMBs in South Africa so you can migrate with confidence and minimal disruption.

    Phase 1 — Plan and assess

    1. Define objectives and scope

    Start by defining why you are migrating and what success looks like. Common goals include replacing legacy email, enabling remote access, standardising collaboration tools, or improving security. Set measurable outcomes such as acceptable downtime, user adoption targets, and compliance needs.

    2. Inventory users, devices and data

    Compile a clear inventory: number of users, mailboxes, file servers, SharePoint sites, OneDrive usage, and line-of-business applications that integrate with Microsoft 365. Note device types and operating systems in use. For many South African SMBs this inventory highlights licensing needs and potential compatibility issues.

    3. Assess current environment and dependencies

    Review your current email system (Exchange on-premises, hosted IMAP, or third party), identity setup (Active Directory), and network bandwidth. Identify dependencies like printers, ERP systems or legacy apps that rely on on-premises servers.

    4. Choose licences and architecture

    Select the Microsoft 365 licences that match your needs—Business Basic, Business Standard, or Business Premium are common for SMBs. Decide on identity model: cloud-only Azure AD or hybrid Azure AD Connect if you have an on-premises Active Directory.

    Phase 2 — Prepare and secure

    1. Prepare identity and authentication

    • Set up Azure Active Directory and plan user accounts.
    • If using hybrid, configure Azure AD Connect and test synchronisation.
    • Enforce multi-factor authentication (MFA) for all admin and user accounts.

    2. Establish governance and policies

    Create policies for mailbox sizes, retention, external sharing, device management and data loss prevention (DLP). Governance prevents sprawl and keeps data secure—especially important for clients and suppliers in Gauteng and elsewhere.

    3. Secure your environment

    • Enable Conditional Access policies to restrict access by location or device compliance.
    • Deploy Microsoft Defender for Office 365 or equivalent to protect against phishing and malware.
    • Configure Exchange Online Protection and set anti-spam rules.

    4. Network and bandwidth checks

    Test your internet uplink and latency. Microsoft 365 is cloud-first so ensure your connection can handle email, Teams calls and file syncing. Consider split-tunnelling VPN rules or ExpressRoute for high-availability needs in larger SMBs.

    Phase 3 — Migrate data

    1. Email migration

    Choose the right migration method: cutover, staged, hybrid, or IMAP migration. Cutover suits smaller organisations; hybrid or staged approaches help when keeping some on-premises mailboxes is required. Test migrations with a small pilot group first.

    2. Files and SharePoint migration

    Map on-premises file shares to OneDrive and SharePoint libraries. Use migration tools (Microsoft SharePoint Migration Tool or trusted third-party tools) to preserve permissions and metadata. Communicate any folder structure changes and expected sync behaviour to users.

    3. Teams and collaboration content

    Plan how channels, files and Teams apps will be moved or recreated. Some third-party tools can preserve Teams history, but often you’ll need to archive legacy content and provide users with clear steps for rebuilding where necessary.

    Phase 4 — Test, train and cutover

    1. Pilot group testing

    Run a pilot with representative users across departments. Validate mailbox access, file sync, Teams calls and line-of-business integrations. Use pilot feedback to refine migration steps, communications and training materials.

    2. User communication and training

    • Schedule migration windows and inform staff well in advance.
    • Provide short how-to guides: accessing email, using OneDrive, joining Teams meetings, and reporting issues.
    • Offer live Q&A sessions or drop-in clinics during the first week post-migration.

    3. Execute cutover and validation

    Perform the cutover during low-activity hours. Verify DNS records, mail flow, and that all users can sign in. Monitor performance for 48–72 hours and be ready to rollback or apply quick fixes if critical problems arise.

    Phase 5 — Post-migration and optimisation

    1. Monitor and resolve issues

    Use the Microsoft 365 admin centre and Defender dashboards to monitor incidents. Track support tickets and ensure timely response—fast resolution is core to RandTech IT’s approach, avoiding lengthy learning-on-client-time delays.

    2. Optimise licences and costs

    Review licence usage after a month and reassign or downgrade where appropriate to control costs. Keep an eye on storage consumption and upgrade plans if needed—budget in ZAR for any additional licences or third-party tools.

    3. Implement ongoing security and backup

    • Enable regular reporting and security alerts.
    • Consider third-party backup for Exchange Online, SharePoint and OneDrive to meet retention policies.
    • Run regular phishing simulations and security awareness training.

    Quick migration checklist (summary)

    1. Define objectives, scope and success criteria.
    2. Inventory users, mailboxes, file shares and apps.
    3. Choose licences and identity model.
    4. Configure Azure AD and MFA.
    5. Set governance, retention and sharing policies.
    6. Test network bandwidth and connectivity.
    7. Perform pilot migrations for email and files.
    8. Train users and schedule cutover windows.
    9. Monitor, fix issues and validate functionality.
    10. Optimise licences and implement backups.

    FAQ

    How long does a Microsoft 365 migration take for an SMB?

    Duration varies: small businesses can complete a basic migration in a few days to a couple of weeks. Larger SMBs or those with complex integrations and hybrid setups may take several weeks. Proper planning shortens disruptions.

    Will users lose email or files during migration?

    When planned correctly and using staged or hybrid approaches, data loss is avoidable. Always run pilot migrations, verify mail flow and keep backups. Communicate expected read-only periods if any.

    Do I need additional licences for security tools?

    Core Microsoft 365 licences include baseline security features, but you may want Business Premium or add-ons like Defender for Office 365 depending on risk. Assess your regulatory needs and threat profile before purchasing.

    Can RandTech IT manage the whole migration for us?

    Yes. RandTech IT specialises in managed migrations for South African SMBs, providing planning, secure execution and fast, experienced support to reduce downtime and learning-on-client-time delays.

    What about backups and data retention?

    Microsoft retains some data for set periods, but third-party backup solutions are recommended for long-term retention, compliance, or rapid restores. Include backup strategy in your migration plan.

    Conclusion

    Migrating to Microsoft 365 brings productivity and security benefits, but requires careful planning, testing and user support. Follow this checklist to reduce risk and ensure a smooth transition for your South African SMB. If you want a migration handled by experienced engineers who prioritise fast resolution, RandTech IT can help.

    Contact RandTech IT today for practical, experienced assistance with your Microsoft 365 migration. Our team will assess your environment, plan the migration and deliver fast, reliable support so your business keeps running.

  • Common Microsoft 365 Migration Mistakes and How to Avoid Them

    Common Microsoft 365 Migration Mistakes and How to Avoid Them

    Introduction

    Migrating to Microsoft 365 can deliver productivity, collaboration and security benefits for South African small and medium-sized businesses. But migrations that look simple on paper often go off track — causing downtime, data loss, or compliance headaches. This guide highlights the most common Microsoft 365 migration mistakes, explains why they happen, and gives practical steps SMBs can take to avoid them.

    1. Skipping a Proper Migration Assessment

    One of the biggest risks is starting a migration without a clear assessment of your current environment.

    Why this is a mistake

    Without an inventory of users, mailboxes, file shares and third-party integrations you can’t plan capacity, timelines or identify potential blockers. Unexpected issues during migration increase costs and extend downtime.

    How to avoid it

    • Conduct a discovery: document email volumes, file storage locations, custom applications and identity systems.
    • Map dependencies: list printers, line-of-business apps and integrations that rely on on-prem services.
    • Assess bandwidth and performance: check internet links in Johannesburg/Gauteng offices if relevant for upload capacity.

    2. Poor Identity and Authentication Planning

    Identity configuration drives access and security in Microsoft 365. Mistakes here cause login failures and increase security risk.

    Common problems

    • Not deciding between cloud-only accounts and hybrid Azure AD Connect early enough.
    • Skipping multi-factor authentication (MFA) planning and user experience testing.
    • Poor password and single sign-on configuration causing lockouts.

    Best practices

    • Choose and document your identity model (cloud-only, hybrid, AD FS) before migration.
    • Enable MFA for all administrators and progressively for users, with clear communications and training.
    • Test authentication flows and SSO with a small pilot group in your Gauteng office to validate performance and experience.

    3. Underestimating Data Migration Complexity

    Data migrations — especially from mixed sources like on-prem file servers, Google Workspace or legacy email systems — are often trickier than expected.

    Typical consequences

    • Missing files or metadata, broken folder permissions, or duplicate files.
    • Longer transfer times due to bandwidth limits or throttling.

    How to manage data migration

    • Prioritise what moves first: critical mailboxes and active document libraries should be migrated before archival data.
    • Use proven migration tools and validate them in a test run with representative datasets.
    • Plan for throttling: schedule large transfers outside business hours and consider seeding with physical transfer options if volumes are very large.

    4. Neglecting Security and Compliance Settings

    Migrating to Microsoft 365 is an opportunity to improve security — but many organisations simply replicate insecure on-prem configurations.

    What to watch for

    • Default sharing settings that expose files externally.
    • Missing retention, backup or eDiscovery policies required for compliance.
    • Not configuring conditional access and endpoint management for mobile users.

    Practical steps

    • Review and adjust external sharing policies and default link permissions before going live.
    • Configure retention and backup strategies — Microsoft 365 is not a backup by default.
    • Use conditional access and Intune to secure devices that access corporate data, especially if staff work from multiple Johannesburg locations.

    5. Failing to Communicate and Train Users

    Technical success is wasted if users can’t work after migration. Change management is essential.

    Common outcomes of poor communication

    • High support calls, frustration and productivity loss.
    • Users resorting to shadow IT or insecure workarounds.

    What to include in your plan

    • Clear timelines and expected downtime windows communicated well in advance.
    • Simple user guides for common tasks (Outlook configuration, OneDrive sync, Teams basics).
    • Hands-on support for the first 48–72 hours after cutover, and a pilot group to identify issues early.

    6. Ignoring Backup and Recovery Planning

    Relying solely on Microsoft’s native safeguards without an independent backup exposes you to accidental deletion, ransomware, or retention gaps.

    Recommendations

    • Implement third-party backup for Exchange Online, SharePoint and OneDrive where retention and point-in-time recovery matter.
    • Document recovery RTOs and RPOs and test restores before and after migration.

    7. Overlooking Network and Endpoint Readiness

    Network bottlenecks and outdated endpoints can cause poor performance post-migration, harming user uptake.

    Checks to perform

    • Verify internet link capacity, especially at peak office hours — consider LTE/5G failover for small Johannesburg offices.
    • Ensure workstations meet requirements for the Microsoft 365 apps and have supported OS and patch levels.

    8. Not Using a Phased Migration Approach

    Big-bang migrations increase risk. A phased approach reduces impact and gives time to fix issues.

    Recommended phased model

    1. Discovery and pilot: small group migrates first.
    2. Core services: mailboxes and critical file shares.
    3. Remaining users and archive data.
    4. Decommission old systems after validation.

    Checklist: Pre-Migration Essentials

    • Complete discovery of users, apps and data sources.
    • Decide identity model and test authentication flows.
    • Secure licenses and map features to user roles.
    • Plan backups, retention and compliance policies.
    • Communicate timelines and provide training resources.
    • Run pilot migrations and performance tests.

    FAQ

    1. How long does a typical Microsoft 365 migration take for an SMB?

    Times vary: small organisations can complete a basic migration in days, while complex environments with many integrations or large data volumes can take weeks. A proper assessment gives a realistic timeline.

    2. Do I need third-party tools to migrate to Microsoft 365?

    Not always, but third-party migration and backup tools often reduce risk, preserve metadata and speed transfers — especially when moving from non-Microsoft systems.

    3. Will Microsoft 365 protect my company from ransomware?

    Microsoft 365 includes strong security features, but it isn’t a complete backup solution. Combine built-in protection with endpoint security, conditional access and independent backups for best results.

    4. Can we keep our existing on-premises Active Directory?

    Yes. Hybrid identity with Azure AD Connect is common and lets you keep on-premises AD while taking advantage of Microsoft 365. Plan synchronisation and authentication carefully to avoid conflicts.

    5. What are common hidden costs during migration?

    Costs can come from extended consulting hours, additional licences, third-party tools, increased internet capacity, and user downtime. Budget for contingencies.

    Conclusion

    A successful Microsoft 365 migration for South African SMBs requires planning, security-first thinking and clear user communication. Avoiding common mistakes — like skipping discovery, neglecting identity and failing to back up data — reduces downtime and protects your business. Phased migrations, pilot testing and using proven tools make transitions smoother and faster.

    Get practical, experienced help. RandTech IT prioritises quick resolution by experienced engineers so your migration runs efficiently, without on-the-job learning. Contact RandTech IT to discuss a migration plan tailored to your business needs.

  • How to Secure Microsoft 365 Against Account Takeover

    How to Secure Microsoft 365 Against Account Takeover

    Introduction

    Account takeover in Microsoft 365 (M365) is a growing threat for South African small and medium-sized businesses. An attacker with a compromised M365 account can read emails, access files in OneDrive and SharePoint, and impersonate staff to trick customers or suppliers. That can lead to financial loss, reputational damage and costly recovery work.

    This guide explains practical, prioritised steps you can apply today to reduce the risk of account takeover. The recommendations are written for SMBs in South Africa and assume limited internal IT resources — the focus is on effective controls you can implement quickly or get help to deploy.

    Understand the attack paths

    Before you act, know how attackers typically gain access:

    • Phishing: deceptive emails or links that harvest credentials or MFA codes.
    • Credential stuffing: using leaked passwords from other services.
    • Brute force and password spray: automated attempts against weak passwords.
    • Compromised devices: malware on a workstation that steals tokens or session cookies.
    • Poorly configured admin accounts: excessive privileges or missing protections.

    Essential steps to secure Microsoft 365

    These controls offer the best balance of protection and practicality for SMBs.

    1. Enforce Multi-Factor Authentication (MFA)

    MFA blocks most account takeover attempts even if a password is compromised. Require MFA for all users, starting with administrators and finance staff. Use an authenticator app or hardware security keys rather than SMS when possible, as SMS is vulnerable to SIM swap attacks.

    2. Configure Conditional Access policies

    Azure Active Directory Conditional Access lets you apply rules based on location, device state and risk. For example:

    • Block sign-ins from high-risk countries or anonymising proxies.
    • Require compliant or hybrid-joined devices to access sensitive apps.
    • Require MFA for risky sign-ins or high-privilege actions.

    Start with simple, high-impact policies and refine as you learn how they affect users.

    3. Protect privileged accounts

    Limit the number of Global Administrators and use Privileged Identity Management (PIM) where available to provide just-in-time elevation. Ensure admin accounts have dedicated credentials and strict MFA enforcement. Monitor all admin activities and enable audit logging.

    4. Harden authentication and passwords

    Apply these password and identity hygiene measures:

    • Disable legacy authentication protocols that bypass modern MFA.
    • Implement a password policy that prevents reuse of breached credentials (Azure AD Password Protection).
    • Encourage passphrases or use password managers to reduce weak passwords.

    5. Monitor sign-in activity and alerts

    Use Azure AD Identity Protection, Microsoft Defender for Office 365 and Microsoft Defender for Identity if licensed. Monitor for:

    • Unfamiliar locations or impossible travel events.
    • Multiple failed sign-ins or unusual application access patterns.
    • Mass forwarding rules or suspicious mailbox delegations.

    Configure alerting to the right people so incidents are investigated promptly.

    6. Secure email and reduce phishing risk

    Email is the most common vector. Implement standard protections:

    • Enable Exchange Online Protection and anti-phishing policies.
    • Use DKIM, SPF and DMARC to reduce email spoofing.
    • Block external mail forwarding by default and review exceptions.

    Complement technical controls with user education focused on recognising phishing attempts and verifying payment requests.

    7. Backup critical Microsoft 365 data

    M365 provides redundancy but not traditional point-in-time backups for user-deleted or modified data. Use a third-party backup solution for Exchange, OneDrive, SharePoint and Teams to ensure you can recover from account misuse, mass deletions or ransomware.

    8. Secure endpoints and networks

    Protect the devices users sign in from:

    • Keep Windows and other OS patches current.
    • Use endpoint protection with anti-malware and behavioural detection.
    • Require disk encryption and strong access controls on laptops.

    Where possible, prevent unmanaged devices from accessing sensitive data using Conditional Access.

    Operational practices and incident readiness

    Regular review and least privilege

    Review user and app permissions quarterly. Remove stale accounts and reduce mailbox delegates. Apply least privilege to applications that request access to M365 data.

    Logging, retention and playbooks

    Retain audit logs for investigation and compliance. Create an incident response playbook that covers detection, containment, account recovery and notification. Ensure a trained person or external partner can act quickly outside normal hours.

    User training and simulated phishing

    Regular, practical training reduces risk. Run occasional phishing simulations to measure awareness and target further coaching where users click malicious links or disclose credentials.

    Cost-conscious planning for South African SMBs

    Budgeting for M365 security can be challenging. Focus on cost-effective, high-impact controls first: MFA, disabling legacy auth, email protections and backups. Many protections are included in Microsoft 365 Business Premium; evaluate whether upgrading licensing or using targeted third-party tools gives better value than reactive recovery work.

    If internal capacity is limited, engage a trusted local partner who can implement Conditional Access, PIM and backups with minimal disruption. RandTech IT specialises in hands-on support so your team isn’t used as a learning environment — we implement proven configurations quickly so you can get back to business.

    Quick checklist to secure Microsoft 365

    • Enforce MFA for all users — avoid SMS where possible.
    • Disable legacy authentication protocols.
    • Apply Conditional Access for risky locations and compliant devices.
    • Restrict and monitor Global Admins; enable PIM if available.
    • Enable Exchange anti-phishing, SPF/DKIM/DMARC.
    • Deploy third-party backups for Exchange, OneDrive and SharePoint.
    • Train staff on phishing and run simulations.
    • Keep endpoints patched and protected.

    Frequently asked questions

    How quickly can MFA be rolled out?

    MFA for administrators can be enabled in hours. A staged rollout for all users, including support for authenticator apps and tied devices, typically takes several days depending on company size and user readiness.

    Is SMS-based MFA acceptable for small businesses?

    SMS offers better protection than none but is vulnerable to SIM swap attacks. Use authenticator apps or hardware keys for higher-risk accounts like finance and administrators.

    Do I need Microsoft Defender licenses to be secure?

    Defender products add detection and recovery capabilities, but strong baseline controls (MFA, Conditional Access, email protection, backups) provide substantial protection even without premium licences.

    What should I do immediately after detecting an account takeover?

    Contain the incident: block access, reset credentials, revoke active sessions, remove malicious forwarding rules, and restore affected data from backups. Then perform a root-cause analysis and strengthen the controls that failed.

    Can RandTech IT help implement these controls?

    Yes. RandTech IT offers hands-on implementation, monitoring and incident response for South African SMBs. We prioritise experienced engineers who implement securely and quickly.

    Conclusion

    Securing Microsoft 365 against account takeover is achievable for South African SMBs with a focused set of controls: enforce MFA, apply Conditional Access, protect privileged accounts, secure email and endpoints, and maintain backups. Combine technical controls with user training and clear incident procedures.

    If you need practical, experienced assistance to implement these protections without disrupting your business, contact RandTech IT. We can assess your current M365 configuration, prioritise improvements and implement them quickly so you can operate securely.

    Contact RandTech IT — reach out for a pragmatic, experienced partner to secure your Microsoft 365 environment and reduce the risk of account takeover.

  • Microsoft 365 migration checklist for South African SMBs

    Microsoft 365 migration checklist for South African SMBs

    Introduction

    Migrating to Microsoft 365 is a smart move for South African small and medium-sized businesses (SMBs) looking to modernise email, collaboration and security. But a poorly planned migration can cause downtime, data loss and user frustration. This Microsoft 365 migration checklist gives a clear, step-by-step approach tailored to the needs of SMBs in South Africa, so you can move confidently with minimal disruption.

    1. Pre-migration planning

    Thorough planning reduces surprises. Treat migration as both a technical and people project.

    Define goals and scope

    • List what you want from Microsoft 365: hosted email, Teams, SharePoint, OneDrive, device management, or advanced security.
    • Decide which users, departments and data sets move in the first phase.
    • Set success criteria such as acceptable downtime, device compatibility and post-migration performance.

    Assemble a project team

    • Assign an internal project lead and technical contact for day-to-day coordination.
    • Include end-user representatives to capture practical needs and minimise resistance.
    • Consider engaging experienced managed services engineers—faster resolution reduces business risk.

    Budget and licences

    Map current costs and estimate Microsoft 365 licence needs. In South Africa, factor VAT and local payment models. Choose licences that match feature needs—E3/E5 for larger security or compliance needs, Business Standard or Premium for typical SMBs.

    2. Technical discovery

    Understand your current IT environment before you move anything.

    Inventory users and data

    • Create a user list with roles, mailbox sizes and device types.
    • Identify data sources: on-premises Exchange, file servers, local accounts and third-party cloud services.
    • Flag legacy applications that integrate with email or Active Directory.

    Assess network and bandwidth

    Microsoft 365 relies on stable internet connections. Measure upload speeds at branch offices and remote sites. Plan for peak usage—consider adding temporary bandwidth or using scheduled migration windows to reduce impact.

    Check identities and authentication

    Decide on identity model: cloud-only, synchronized identities (Azure AD Connect) or federated authentication. For most SMBs, Azure AD Connect with password hash sync provides a balance of convenience and control.

    3. Security and compliance

    Security must be part of the migration, not an afterthought.

    Set baseline security controls

    • Enable multi-factor authentication (MFA) for all administrator accounts immediately.
    • Deploy conditional access policies for high-risk sign-ins and external access.
    • Configure basic data loss prevention (DLP) and retention policies suitable for your sector.

    Backup and retention

    Microsoft 365 includes resiliency, but native retention is not a full backup strategy. Ensure you have third-party or managed backups for Exchange, SharePoint and OneDrive where required by your business continuity plans.

    4. Migration approach and timelines

    Choose a migration method that matches your environment and risk tolerance.

    Common migration methods

    • Cutover migration: suitable for very small organisations moving all mailboxes at once.
    • Staged migration: moves batches of users over time—good for expanding SMBs.
    • Hybrid migration: for organisations keeping some mailboxes on-premises while moving others.
    • Third-party tools: helpful for complex data, PST migration or cross-tenant moves.

    Plan a realistic timeline

    Build time for discovery, pilot, migration, validation and user training. For most SMBs, a staged migration over several weekends reduces risk and preserves productivity.

    5. Pilot and testing

    Run a pilot with a small group before mass migration.

    Pilot checklist

    • Select pilot users from different roles and locations.
    • Test mail flow, calendar sharing, Teams meetings and file access.
    • Validate mobile access, conditional access, and MFA enrolment.
    • Collect feedback and adjust runbook and training materials.

    6. Communication and user training

    Communicate clearly and train early to reduce helpdesk calls.

    Prepare users

    • Notify users of timelines, expected downtime and support contacts in advance.
    • Provide short how-to guides for Outlook, Teams and OneDrive basics.
    • Offer drop-in sessions or online training—practical time-saving tips reduce resistance.

    7. Migration execution

    Run migrations in controlled waves with monitoring and rollback plans.

    Execution best practices

    • Perform migrations outside core business hours where possible, or over weekends.
    • Monitor mail queues, sync health and authentication logs during the cutover.
    • Keep a verified restore point to revert if critical issues arise.

    Post-migration validation

    Check that mail flow works, calendars are intact, Teams channels are accessible and file permissions are preserved. Confirm mobile devices can connect and that MFA and conditional access behave as expected.

    8. Post-migration optimisation

    After the move, refine settings and hand over to operations.

    Security hardening and governance

    • Tune conditional access, DLP and retention policies based on observed behaviour.
    • Implement role-based administrative access and monitor privileged account activity.

    Ongoing support and training

    Provide ongoing user support for the first 30–90 days. Gather feedback, update documentation and run refresher training sessions to boost adoption.

    Checklist summary

    1. Define goals, scope and budget.
    2. Inventory users, mailboxes and files.
    3. Assess network, devices and identity model.
    4. Set security baseline: MFA, conditional access, backups.
    5. Choose migration method and plan timelines.
    6. Run a pilot and validate results.
    7. Communicate and train users beforehand.
    8. Execute migrations in waves with monitoring and rollback plans.
    9. Validate, optimise and hand over to operations.

    FAQ

    • How long does a Microsoft 365 migration take?

      Time varies by size and complexity. For small SMBs it can be a few days; more commonly staged migrations across weeks minimise risk.

    • Do we need to keep on-premises servers?

      Not always. Many SMBs go cloud-only. Hybrid setups remain an option if specific services or compliance needs require on-premises systems.

    • What licences do South African SMBs typically choose?

      Business Standard or Business Premium suit most SMBs. Larger organisations or those with advanced security/compliance needs may prefer E3/E5.

    • Will my email addresses change?

      Your primary email addresses can remain the same. Plan DNS and MX record updates to switch mail flow with minimal downtime.

    • Is third-party backup necessary?

      Yes. Microsoft 365 provides redundancy, but third-party backups help meet retention, legal discovery and recovery requirements.

    Conclusion

    A well-structured Microsoft 365 migration checklist keeps your South African SMB focused on business continuity, security and user adoption. Proper discovery, a pilot phase and clear communication are the keys to a smooth transition. RandTech IT prioritises fast resolution by experienced engineers, helping you migrate with minimal disruption and practical support when you need it most.

    If you’d like experienced help planning and executing your Microsoft 365 migration, contact RandTech IT. Our team provides hands-on support across Johannesburg and Gauteng to ensure a secure, efficient migration that lets your business get back to work fast.

  • Why Microsoft 365 Still Needs Independent Backup

    Why Microsoft 365 Still Needs Independent Backup

    Introduction

    Microsoft 365 is the backbone of many South African small and medium-sized businesses. It offers email, collaboration, file storage and productivity tools in a single subscription — a compelling value for organisations in Johannesburg and beyond. However, Microsoft’s shared responsibility model means that some critical aspects of data protection remain the customer’s responsibility.

    This article explains why Microsoft 365 still needs independent backup, the common risks businesses face, compliance and recovery considerations in a South African context, and practical steps to implement a resilient backup strategy.

    What Microsoft 365 protects — and what it doesn’t

    Microsoft protects the availability of the Microsoft 365 infrastructure and provides built-in recovery tools for certain scenarios. But that protection is not the same as a comprehensive backup designed for long-term retention, point-in-time restores and legal discovery.

    Microsoft’s strengths

    • High availability and geographically distributed infrastructure.
    • Redundancy to keep services running during outages.
    • Basic restore capabilities for deleted items within retention windows.

    Where independent backup is needed

    • Accidental deletion beyond retention periods.
    • Malicious insider actions or compromised accounts.
    • Ransomware that encrypts or deletes cloud-hosted files.
    • Legal and compliance requirements for long-term retention and eDiscovery.
    • Retention gaps when subscriptions or licences change.

    Common data loss scenarios for South African SMEs

    Understanding typical failure modes helps prioritise backup decisions.

    Human error

    Employees frequently delete emails or documents accidentally. If the deletion passes Microsoft’s retention window or version history, the content can be gone for good without an independent backup.

    Security incidents

    Compromised accounts and ransomware attacks are rising in South Africa. Attackers who gain access to Microsoft 365 can delete or alter content across Exchange, SharePoint and OneDrive. An immutable, independent backup helps recover clean copies without paying ransom.

    Compliance and litigation

    SMEs working with regulated industries or on public contracts may need to retain records for specific periods. A third-party backup provides defensible retention policies and easier eDiscovery than relying on native tools alone.

    Key benefits of independent Microsoft 365 backup

    • Point-in-time restores for mailboxes, SharePoint sites and OneDrive files.
    • Longer, custom retention schedules to meet legal requirements.
    • Protection against account compromise and ransomware.
    • Operational simplicity for restores — less downtime and faster recovery.
    • Separation of duties: backups isolated from the primary tenant reduce single points of failure.

    What to look for in a Microsoft 365 backup solution

    Not all backup offerings are equal. When evaluating options for a South African SME, prioritise these capabilities:

    Comprehensive coverage

    Ensure the solution covers Exchange Online, SharePoint Online, OneDrive for Business, Teams and group mailboxes. Verify it preserves metadata, permissions and version history where possible.

    Retention flexibility and immutability

    Choose solutions that allow custom retention periods and support immutable storage to defend against tampering or accidental deletion.

    Efficient storage and cost control

    Look for deduplication, incremental backups and pricing that aligns with your budget. For SMEs, predictable monthly costs in ZAR (Rands) make planning easier.

    Fast, granular restore options

    Ability to restore single items, full mailboxes, or entire SharePoint sites quickly is crucial to reduce business disruption.

    Local expertise and support

    Work with a partner who understands South African business conditions, compliance expectations and can offer hands-on support when you need it.

    Implementing a practical backup strategy

    Below is a practical approach tailored for South African SMEs that balances protection with cost and operational needs.

    1. Assess your data and risk

    Identify critical data stores in Microsoft 365 and classify them by business impact. Prioritise mailboxes of key personnel, financial records, contracts and project documents stored in SharePoint.

    2. Define retention and recovery objectives

    • Recovery Time Objective (RTO): how quickly you need data restored.
    • Recovery Point Objective (RPO): how much data loss is acceptable.
    • Retention periods driven by compliance and business needs.

    3. Choose the right backup product

    Select a solution that covers your selected workloads, supports immutability and fits your budget. Prefer vendors with local or regional support partners.

    4. Test backups and restores regularly

    Schedule periodic restore tests to confirm recoverability. Testing reduces surprises during real incidents and keeps your team confident in the process.

    5. Combine with strong security practices

    Backups are part of a broader security posture. Implement MFA, least privilege access, conditional access policies and effective endpoint protection to reduce attack surfaces.

    Cost considerations for South African SMEs

    Budgeting for independent backup need not be prohibitive. Many backup providers offer tiered plans suitable for SMEs, with predictable monthly pricing in ZAR. Factor in:

    • Licence and per-user costs.
    • Storage consumption driven by retention and change rates.
    • Support and managed services if you prefer offloading administration.

    Working with a trusted local MSP can simplify procurement, implementation and ongoing support — avoiding costly mistakes and time spent on in-house management.

    Frequently asked questions

    Does Microsoft not back up my data automatically?

    Microsoft maintains infrastructure availability and short-term recovery capabilities, but it does not take responsibility for long-term retention, point-in-time restores beyond native retention windows, or protection against deliberate deletion by users.

    How long does Microsoft retain deleted items?

    Retention varies by service and configuration. Native recovery windows may be short or dependent on specific retention policies — which can leave gaps for organisations needing longer-term archives.

    Will having a backup protect me from ransomware?

    An independent, immutable backup is a key defence against ransomware because it enables recovery to a clean state without paying a ransom. Backups must be properly secured and tested to be effective.

    Can I manage backups myself or should I use a managed service?

    SMEs can use self-managed solutions, but many benefit from a managed service that brings experienced engineers, local support and faster resolution — freeing internal teams to focus on core business activities.

    Is independent backup required for compliance?

    Depending on your industry and contractual obligations, independent backup may be necessary to meet retention and eDiscovery requirements. Consult your legal or compliance adviser to confirm obligations.

    Conclusion

    Microsoft 365 provides robust infrastructure and useful native recovery features, but it is not a substitute for independent backup. South African SMEs face specific risks — accidental deletion, ransomware and compliance demands — that call for a deliberate backup strategy.

    Implementing independent backups with clear retention policies, immutable storage and regular restore testing will reduce downtime, protect your data and help meet regulatory obligations. Partnering with a local MSP can simplify the process and provide experienced support when it matters most.

    Contact RandTech IT — if you’d like practical, experienced help protecting your Microsoft 365 data, our engineers prioritise fast resolution and understand the needs of South African SMEs. Reach out to RandTech IT for a straightforward assessment and tailored backup solution.

  • How to Secure Microsoft 365 Against Account Takeover

    How to Secure Microsoft 365 Against Account Takeover

    Introduction

    Account takeover is one of the most common and damaging cyber threats for small and medium-sized businesses (SMBs). For South African organisations using Microsoft 365—email, Teams, OneDrive and SharePoint—a compromised account can expose sensitive client data, interrupt operations and damage reputation. This guide explains practical, cost-effective steps SMBs in South Africa can implement to secure Microsoft 365 against account takeover.

    Understand the risk

    Account takeover typically starts with credential theft—phishing, reused passwords or leaked credentials—and escalates through privilege abuse and lateral movement. In the Microsoft 365 environment, attackers target admin accounts, mailboxes and file shares because they provide broad access.

    Why SMBs are at risk

    • Limited IT resources often mean basic controls are missing.
    • Users may reuse passwords across personal and work accounts.
    • Remote or hybrid work increases login attempts from varied locations.

    Core controls to prevent account takeover

    Start with these high-impact controls. They’re practical for small teams and deliver measurable protection.

    1. Enforce multi-factor authentication (MFA)

    MFA is the single most effective control to prevent account takeover. Require it for all users, not just admins. Use app-based authenticators or hardware tokens rather than SMS when possible, since SMS can be intercepted.

    2. Apply conditional access policies

    Conditional access lets you require stronger authentication or block access based on risk factors such as location, device compliance and sign-in risk. For Johannesburg- or Gauteng-based offices, set trusted locations and restrict high-risk countries.

    3. Harden admin accounts

    • Use dedicated admin accounts: no email, no regular browsing.
    • Require MFA and stronger authentication for all admin roles.
    • Limit the number of users with Global Administrator privileges.

    4. Enforce strong password policies and passphrases

    Encourage passphrases and ban legacy patterns like “Password123”. Use Azure AD password protection to block common or compromised passwords and consider passwordless options like Windows Hello for Business or FIDO2 security keys for critical users.

    5. Enable mailbox and audit logging

    Turn on unified audit logging and mailbox auditing. Logs help you detect suspicious activity—like mass forwarding rules or mailbox delegation—that often accompany account takeover.

    Detection and response

    Preventive controls reduce risk, but detection and response minimise damage if an account is compromised.

    Monitor sign-in activity

    Regularly review sign-in reports in the Azure portal. Look for unusual patterns such as sign-ins from unexpected countries, impossible travel indicators or repeated failed attempts.

    Set up alerting and automated actions

    Configure Microsoft Defender for Office 365 and Azure AD Identity Protection to alert on and automatically respond to risky sign-ins—forcing password resets, blocking access or requiring reauthentication.

    Incident response playbook

    1. Isolate the compromised account: disable sign-in if needed.
    2. Reset the user’s credentials and revoke active sessions and refresh tokens.
    3. Search mailboxes and SharePoint for suspicious forwarding rules, sharing links and data exfiltration.
    4. Restore from known-good backups if data was corrupted or deleted.
    5. Document and review the incident to close gaps in controls.

    Protect email and data

    Email is a primary target. These measures reduce exposure and harden communications.

    Anti-phishing and safe attachments

    • Enable Microsoft Defender for Office 365 anti-phishing policies.
    • Use Safe Links and Safe Attachments to inspect content in transit.

    Control external sharing

    Restrict external sharing on SharePoint and OneDrive where possible. Require link expiration and limit sharing to authenticated users. Regularly review externally shared content and revoke access that’s no longer required.

    Endpoint and device controls

    Compromised endpoints are a common attack vector. Ensure devices connecting to M365 meet minimum security standards.

    Use Microsoft Intune or an MDM solution

    • Enforce device encryption, PINs and updated operating systems.
    • Require device compliance before granting access via conditional access policies.

    Patch and antivirus

    Maintain a patch schedule and run reputable endpoint protection. For smaller firms, managed services can handle these tasks consistently and cost-effectively.

    Policies, training and governance

    Technical controls are essential, but people and processes complete the defence.

    User awareness training

    Phishing simulations and focused training reduce the chances of credential theft. Keep sessions short and practical—show examples relevant to South African business contexts, such as fake SARS or banking emails.

    Least privilege and access reviews

    • Apply least privilege principles across M365 roles and groups.
    • Perform periodic access reviews and remove inactive or unnecessary accounts.

    Backups and business continuity

    Microsoft 365 provides high availability but native retention doesn’t replace backups. Use third-party backup solutions to protect against accidental deletion, ransomware and long-term retention needs.

    Cost-conscious approaches for South African SMBs

    SMBs must balance security with budget. Prioritise controls that yield the greatest reduction in risk for the lowest cost.

    • Start with organisation-wide MFA—low cost, high impact.
    • Adopt conditional access rules for risky scenarios rather than broad licensing upgrades immediately.
    • Consider managed security services to get experienced engineers without hiring full-time specialists.

    If budget is limited, focus on the critical user accounts (finance, HR, executive) first and expand controls as resources allow.

    Conclusion

    Securing Microsoft 365 against account takeover requires a combination of identity controls, device management, monitoring and user education. For South African SMBs, practical steps—MFA, conditional access, admin hardening, logging and backups—deliver meaningful protection without excessive cost. Consistent policies and a tested incident response plan will reduce downtime and business impact when incidents occur.

    FAQ

    1. Is MFA enough to stop account takeover?

    MFA significantly reduces risk but is not a silver bullet. Combine MFA with conditional access, password protection and monitoring for comprehensive protection.

    2. Can my small business afford these controls?

    Many controls—like MFA, password policies and basic logging—are low-cost or included in Microsoft 365 plans. Managed security services can provide expertise cost-effectively for smaller budgets.

    3. How quickly should I respond to a suspected compromise?

    Isolate the account immediately, reset credentials, revoke sessions and search for suspicious activity. Acting within hours can prevent lateral movement and data loss.

    4. Do I need extra backup for Microsoft 365?

    Yes. Native retention may not meet regulatory or recovery needs. Third-party backups protect against accidental deletion, ransomware and long-term retention requirements.

    5. What role does user training play?

    User training reduces the likelihood of credential theft via phishing. Regular, relevant sessions and phishing simulations improve resilience significantly.

    Get practical help

    If your business needs experienced engineers to secure Microsoft 365 quickly and correctly, RandTech IT can help. We focus on fast resolution by seasoned technicians who implement proven controls with minimal disruption. Contact RandTech IT to arrange a review and practical next steps tailored to your environment.