Tag: ransomware

  • How Often Should a Business Test Its Backups?

    How Often Should a Business Test Its Backups?

    How Often Should a Business Test Its Backups?

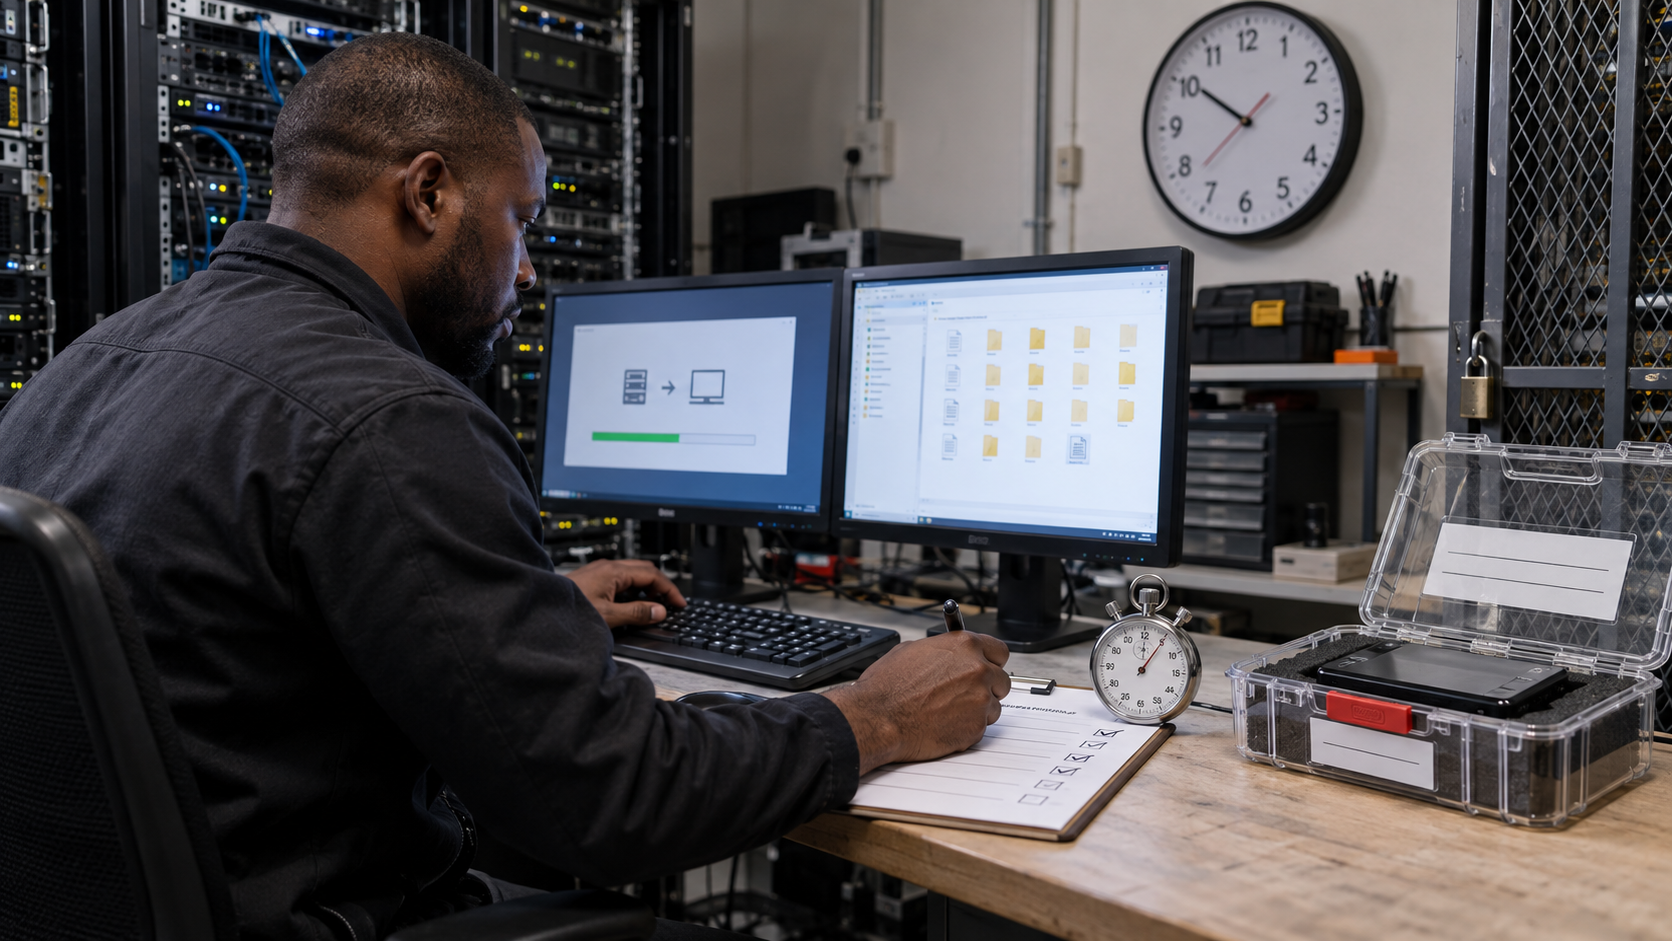
    A business should test important file restores at least quarterly and conduct a broader recovery exercise at least once a year. Higher-risk businesses may need monthly restore tests and more frequent disaster-recovery exercises.

    There is no universal schedule for every organisation. The correct frequency depends on how quickly information changes, how costly downtime would be and whether the business handles regulated or highly sensitive data.

    The central principle is simple: a successful backup notification does not prove that the business can recover.

    Why backups fail when they are needed

    A backup job may display a green status while still failing to protect the information the business considers critical.

    Common problems include:

    • Important folders were never selected
    • A new server or SharePoint site was not added
    • Backup credentials expired
    • Storage reached its capacity
    • Files were already corrupted before being copied
    • The backup is encrypted by the same ransomware
    • Nobody knows the recovery password
    • Restore instructions are outdated
    • The available internet connection is too slow for timely recovery

    These problems are often discovered only when someone urgently needs the data.

    Use more than one type of test

    Backup testing should happen at several levels.

    Monthly automated review

    An IT provider should review failed jobs, warnings, storage capacity and devices that have stopped reporting. This is monitoring rather than a complete recovery test, but it catches obvious problems early.

    Quarterly sample restores

    Restore several representative items, such as:

    • An email
    • A OneDrive folder
    • A SharePoint document
    • An accounting-data file
    • A folder from a server
    • Data belonging to a former employee

    Confirm that the restored information opens correctly and that its permissions and dates are usable.

    Annual recovery exercise

    At least once a year, simulate a more serious outage. Assume a server, primary storage system or Microsoft 365 administrator account is unavailable.

    Measure how long it takes to rebuild access and restore priority services. The exercise should expose unclear responsibilities, missing passwords and unrealistic recovery expectations.

    Businesses that cannot tolerate several hours of downtime should test more frequently.

    Define what must return first

    Not every file has the same operational value.

    An architectural practice may prioritise active project files. A brokerage may need client records, policy documents and email. A retailer may need point-of-sale data and supplier information.

    Your recovery plan should identify:

    • The most critical systems
    • The order in which they must be restored
    • The maximum acceptable data loss
    • The maximum acceptable downtime
    • Who can authorise a recovery
    • Where passwords and encryption keys are stored
    • How staff will work during the outage

    A test should measure performance against these requirements.

    Test Microsoft 365 as well

    Many SMEs back up a local server but overlook Exchange Online, OneDrive, SharePoint and Teams.

    Microsoft provides resilient infrastructure and native recovery tools, but businesses should understand their configuration and recovery limits. Independent Microsoft 365 backup can provide another recovery layer, particularly where deletion or compromise is discovered late.

    Testing should include the restoration of individual cloud files, folders and emails.

    Record and improve every test

    Document what was restored, how long it took and which problems occurred. Assign corrective actions and repeat failed tests.

    RandTech IT helps South African businesses implement monitored backups, test Microsoft 365 and local-data recovery, and create practical disaster-recovery plans.

    If your business has never completed a recorded restore test, you do not yet know whether you have a working backup. Schedule the test before a real emergency sets the deadline for you.
    Source: CISA’s ransomware and backup guidance

  • How to Prevent Ransomware Attacks: Practical Steps for SMEs

    How to Prevent Ransomware Attacks: Practical Steps for SMEs

    Introduction

    Ransomware is a leading cyber threat for South African small and medium-sized businesses (SMEs). An attack can halt operations, expose sensitive data and lead to significant recovery costs. As a business owner or IT decision-maker, knowing how to prevent ransomware attacks is essential. This article offers clear, practical steps tailored to South African SMEs, with a focus on achievable controls, sensible investments and how managed IT support can reduce risk.

    Understand the threat and your risk

    Before implementing controls, assess where your business is most vulnerable. Ransomware typically gains access through phishing emails, unpatched systems, weak remote access configurations and poor backup practices.

    Conduct a basic risk assessment

    • List critical data and systems (financials, payroll, customer data).
    • Identify access points (email, remote desktop, cloud apps).
    • Evaluate business impact if each system became unavailable.

    Understanding impact helps prioritise protections and budget.

    Implement strong endpoint protection

    Endpoints—laptops, desktops and servers—are common ransomware entry points. Effective endpoint protection reduces the chance of successful infection.

    Use reputable antivirus and endpoint detection

    • Choose solutions with real-time protection and behavioural detection.
    • Ensure centralised management so policies and updates are consistent.

    Control administrative privileges

    Limit local admin rights. Users should run day-to-day tasks with standard accounts; elevate privileges only when necessary. Reduced privileges limit malware impact.

    Keep systems and software patched

    Unpatched software is a frequent attack vector. Regular patching prevents attackers exploiting known vulnerabilities.

    Establish a patch management routine

    • Prioritise critical systems and internet-facing services.
    • Schedule regular patch windows and use automated deployment where possible.
    • Test patches on non-critical devices before broad rollout.

    Secure remote access and network architecture

    As more staff use cloud services and remote access from Johannesburg, the Western Cape or elsewhere, securing connections and segmenting networks matters.

    Use VPNs and multi-factor authentication (MFA)

    • Require MFA for remote access, email and admin portals.
    • Use a reputable VPN or secure remote access solution for staff working offsite.

    Network segmentation and least privilege

    Segment your network so a breach in one area does not grant broad access. Keep guest Wi-Fi separate from business systems and isolate critical servers.

    Practice robust backup and recovery

    Backups are the most reliable defence against paying a ransom. A tested recovery plan gets you back to business quickly.

    Follow the 3-2-1 backup rule

    • Keep at least three copies of data.
    • Store backups on two different media types.
    • Keep one copy offsite and offline where possible.

    Test restores regularly

    Backups are only useful if you can restore them. Schedule periodic restore tests and document recovery steps, including estimated recovery time objectives (RTOs).

    Train staff and build a security culture

    Human error remains the top cause of incidents. Practical, role-focused training reduces risk and helps staff recognise attacks early.

    Provide targeted phishing awareness

    • Run short, regular training sessions rather than long annual workshops.
    • Simulate phishing attacks to measure and improve awareness.

    Define clear incident reporting processes

    Make it easy for employees to report suspicious emails or behaviour. Early reporting can stop an attack from spreading.

    Develop policies and incident response plans

    Preparation reduces confusion during an incident. Documented policies and tested response plans shorten downtime and preserve evidence for investigation.

    Key elements of an incident response plan

    • Roles and contact list, including external support (IT partner, legal, forensic).
    • Containment steps to isolate infected devices.
    • Communication templates for staff and customers.
    • Post-incident review and remediation actions.

    Consider cyber insurance and legal obligations

    Cyber insurance can help with recovery costs, but policies vary. Ensure your insurer recognises your security controls and understand requirements under POPIA for personal data breaches.

    Leverage managed IT and security services

    Many SMEs lack the capacity to maintain 24/7 security. A managed service provider (MSP) can deliver experienced, rapid response and continuous monitoring without hiring full-time specialists.

    What a good MSP should provide

    • Proactive patching, endpoint management and security monitoring.
    • Regular backups with tested restores and documented RTOs.
    • Clear escalation procedures and fast incident response by experienced engineers.
    • Guidance on POPIA compliance and local regulatory expectations.

    Practical checklist for immediate action

    1. Enable MFA across email and remote access.
    2. Ensure daily backups with an offline copy and test restores.
    3. Update and patch operating systems and critical apps.
    4. Install centrally managed endpoint protection.
    5. Run quick staff awareness sessions and set an easy reporting channel.

    Conclusion

    Preventing ransomware attacks requires a mix of technology, processes and people-focused measures. For South African SMEs, sensible prioritisation—backups, patching, MFA, staff training and working with an experienced managed IT partner—delivers the best protection for limited budgets. Practical actions today reduce the chance of costly disruption tomorrow.

    FAQ

    1. Can I rely on backups alone to recover from ransomware?

    Backups are essential but must be correctly implemented and tested. Offsite and offline copies plus documented restore procedures are critical. Without tested restores, backups may not help.

    2. Should my business pay the ransom if hit?

    Paying is risky and often discouraged. Payment does not guarantee full recovery or data deletion. In many cases, recovery from verified backups and forensic help is a safer route.

    3. How much should an SME budget for ransomware protection?

    Budgets vary by size and risk profile. Focus on high-impact controls first: backups, MFA, patching and endpoint protection. Working with an MSP can convert fixed costs into predictable monthly fees.

    4. Is cyber insurance worth it for small businesses?

    Cyber insurance can help with costs related to recovery and legal exposure, but policies differ. Ensure your security posture meets insurer requirements and maintain documentation of controls.

    5. How often should we test our incident response plan?

    At minimum, test annually. More frequent tabletop exercises—every six months—are recommended for higher-risk operations or rapidly changing environments.

    6. How quickly can an MSP respond to a ransomware incident?

    Response times depend on the MSP contract. Choose a provider that guarantees fast escalation to experienced engineers and has local knowledge of South African business constraints.

    Contact RandTech IT for experienced, practical assistance. If you want to harden your systems, test your backups or set up an incident response plan, RandTech IT’s engineers can help quickly and professionally. Contact us to discuss a pragmatic security plan tailored to your SME’s needs.